ISO/IEC 27017:2015 – Information Security Controls for Cloud Services
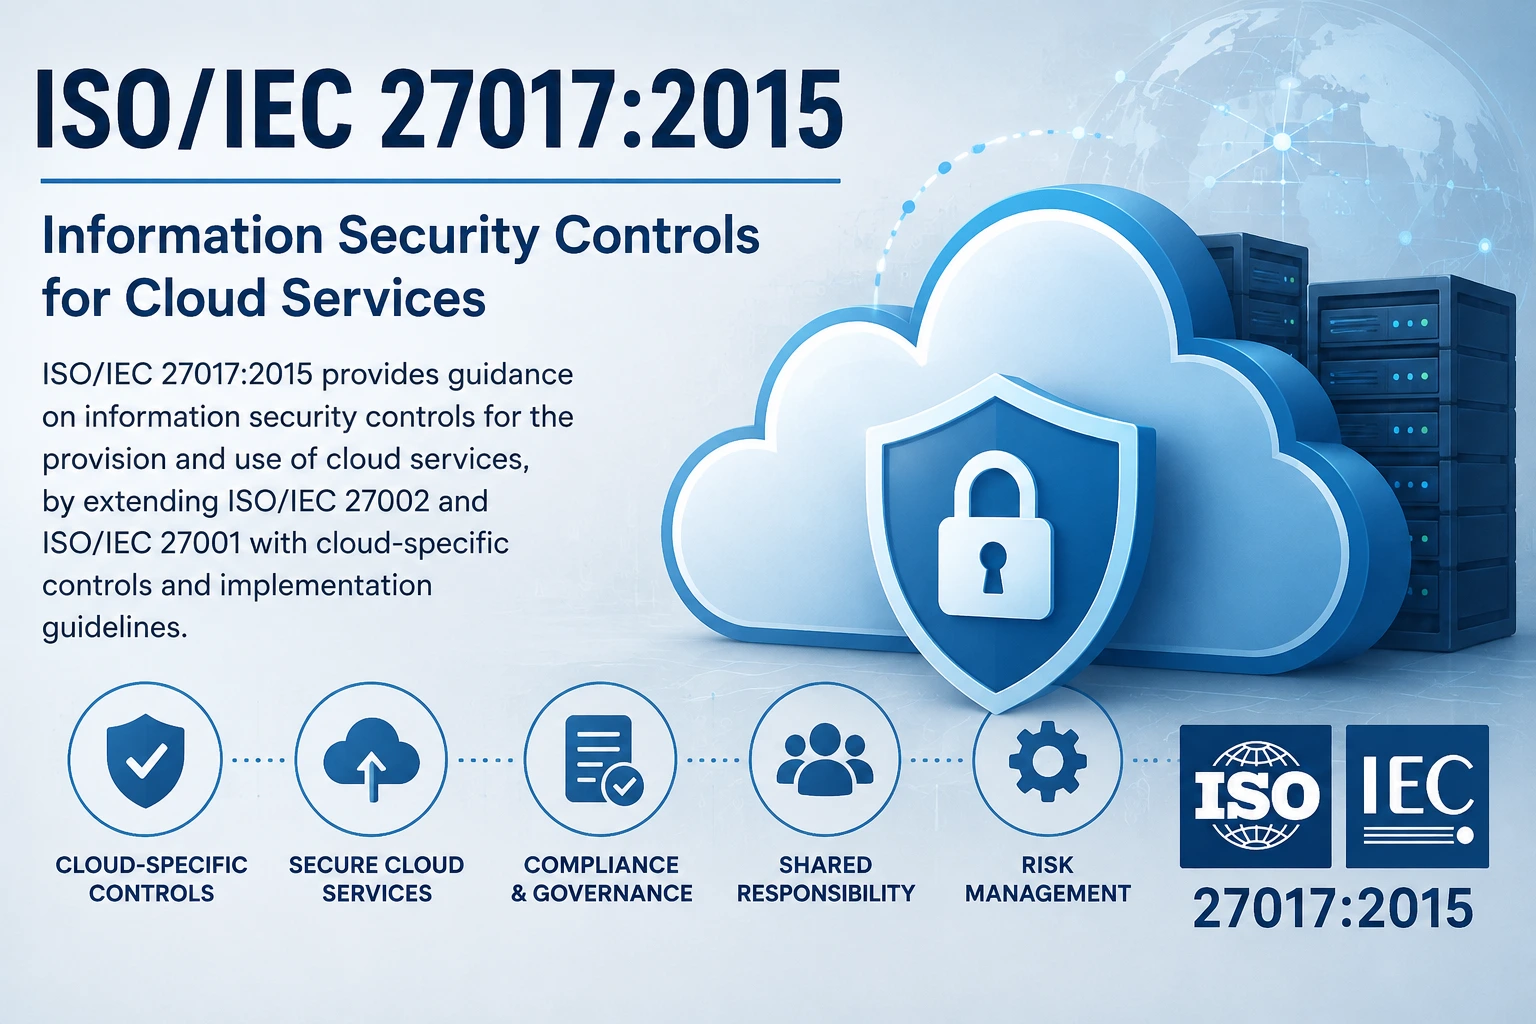
ISO/IEC 27017:2015 provides guidelines and information security controls specifically designed for cloud computing services. It provides additional guidance for implementing security controls for both cloud service providers and cloud service customers.
The standard helps organizations establish appropriate security practices for protecting information and managing security risks associated with cloud-based services and environments.
Benefits of ISO/IEC 27017
- Strengthens cloud information security
- Helps identify and manage cloud security risks
- Improves protection of cloud-based information
- Defines security responsibilities between providers and customers
- Supports secure cloud service management
- Builds customer confidence in cloud security
- Complements ISO/IEC 27001 Information Security Management
Who Can Use ISO/IEC 27017?
ISO/IEC 27017 is particularly relevant to cloud service providers, SaaS companies, data centers, hosting companies, IT service providers, cloud-based application providers, and organizations using or managing cloud computing environments.
Key Areas Covered
The standard provides guidance related to cloud security responsibilities, asset management, access control, virtualization, operational security, customer information protection, and cloud service management.
Contact us to understand the applicable requirements, implementation approach, documentation, and certification options related to ISO/IEC 27017.